Faculty Access Entitlements in IAM for Higher Education IT Teams
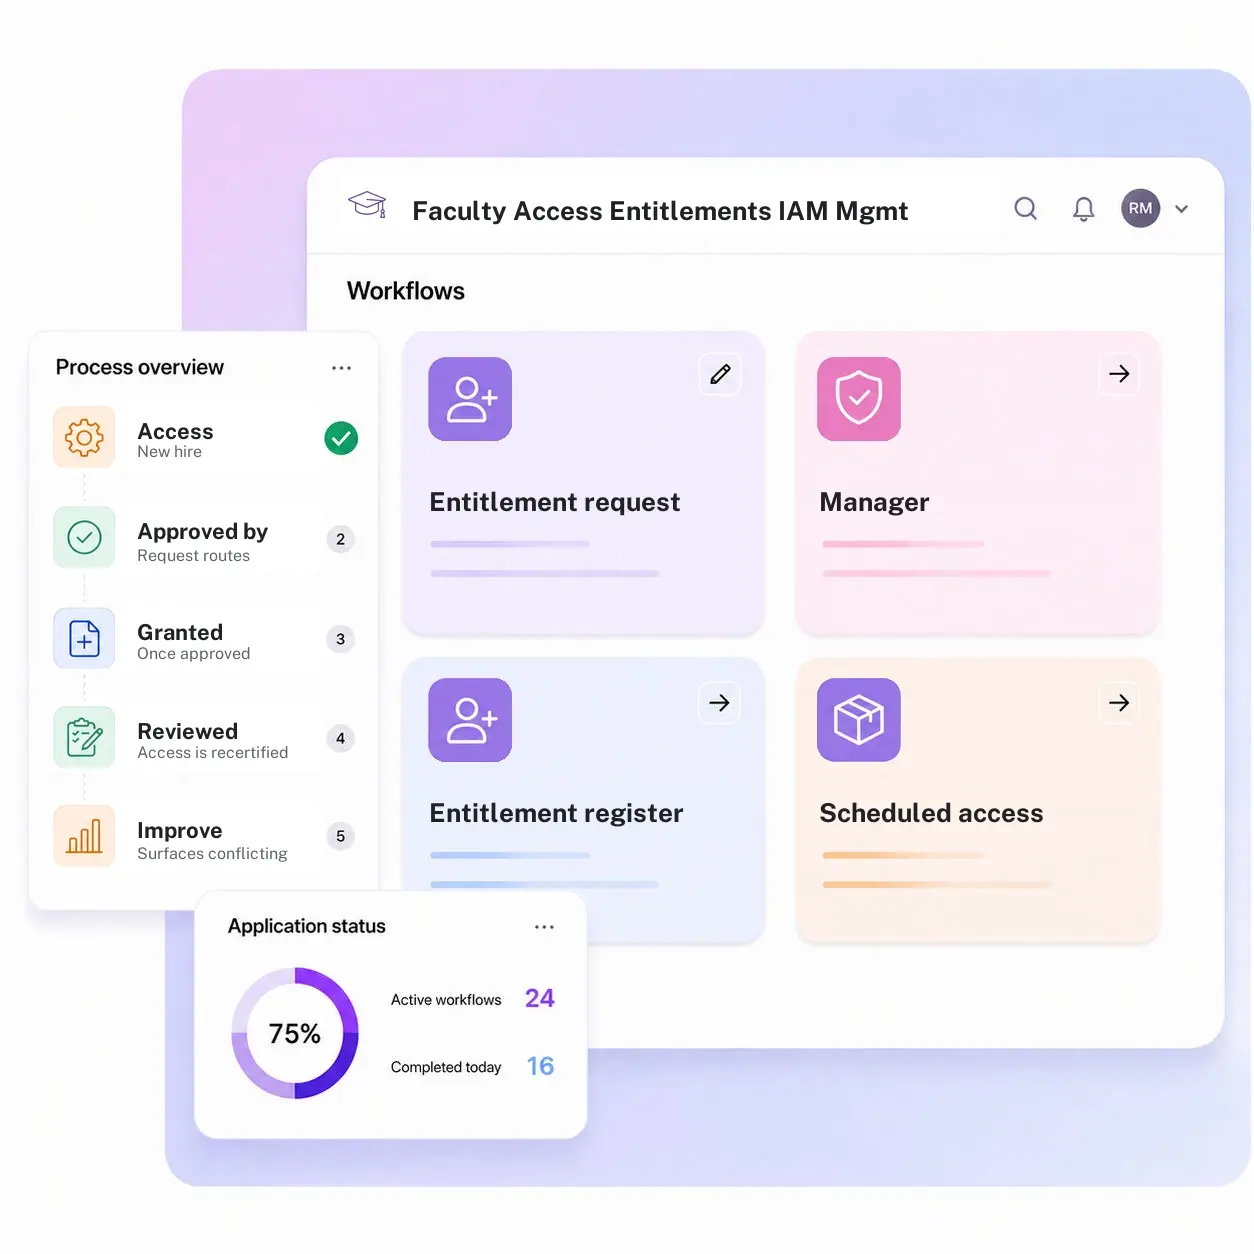
Kissflow routes every faculty access request through the requesting manager and the owning system's administrator, keeps a running entitlement register, reviews standing access on a schedule, and flags a deprovisioning trigger the moment a role ends, so access doesn't outlive the reason it was granted.
Trusted by leading universities worldwide
Entitlements that get reviewed on a schedule, not forgotten after the grant
System access is easy to grant and, historically, hard to remember to take away. A new hire, a department transfer, or a role change each triggers a request for specific system access, and once it's granted, most institutions have no consistent process for revisiting it.
A manager approves an access request without confirming with the system's administrator that it's appropriate for the role. One person ends up able to both submit and approve the same transaction, and nobody catches the conflict until an audit. When a faculty member leaves, deprovisioning depends on whoever handles the separation paperwork remembering every system they had access to.
Kissflow captures every access request against a role or system change, routes it to the requesting manager and the owning system's administrator, keeps an entitlement register, reviews standing access on a recurring schedule, and flags access for removal the moment a role change or separation is recorded. Your IAM platform and Banner or Workday remain the systems that actually hold the access; Kissflow is the governed request, approval, and review layer that decides what gets granted and when it gets revoked.
What standing access looks like without a review cycle
Access outlives the reason it was granted
A role change or department transfer doesn't trigger a review of what access should follow the person and what shouldn't.
Requests get approved without a system-owner check
A manager approves an access request without confirming with the system owner that it's appropriate.
Conflicting entitlements go unnoticed
One person ends up able to both submit and approve the same transaction, and nobody catches it until an audit.
Deprovisioning depends on someone remembering
When a faculty member leaves, access removal depends on whoever handles the paperwork remembering every system they had access to.
Six modules. Built for how faculty access actually needs to be governed.
Every module ships with default forms, approval routing, integrations, and dashboards. Configure each one to your entitlement policy in the visual builder.
Entitlement request capture
A role change, new hire, or department transfer triggers a request for specific system access, with the justification attached.
Manager and system-owner approval
Routes to the requesting department and the owner of the target system before access is granted.
Entitlement register
Keeps a running record of who has access to what, granted when, and under whose approval.
Scheduled access review
Recertifies standing access on a recurring cycle, instead of a one-time grant that never gets revisited.
Automatic deprovisioning trigger
Flags access for removal when a role change, contract end, or separation is recorded.
Access and segregation-of-duties reporting
Surfaces conflicting entitlements and access that has outlived its justification.
From request to system of record in four steps
Submit
A new hire, transfer, or role change generates a request for specific system access.
Review
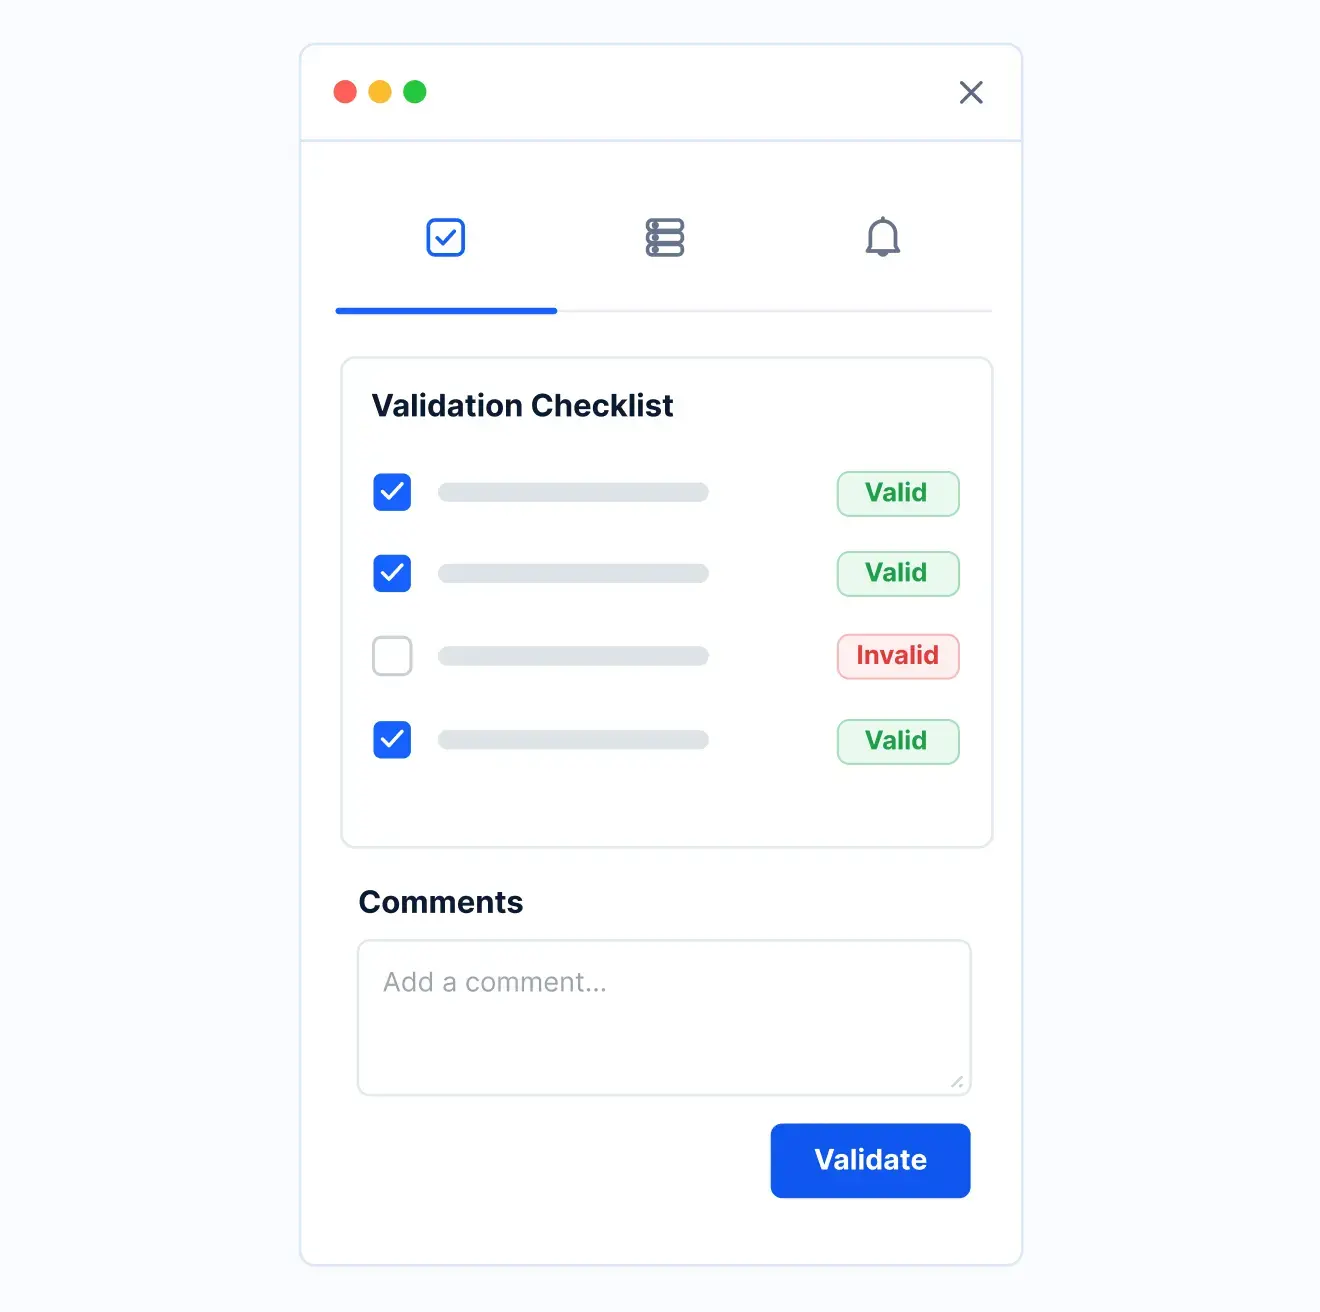
The request routes to the requesting manager and, separately, the owner of the system being requested.
Approve
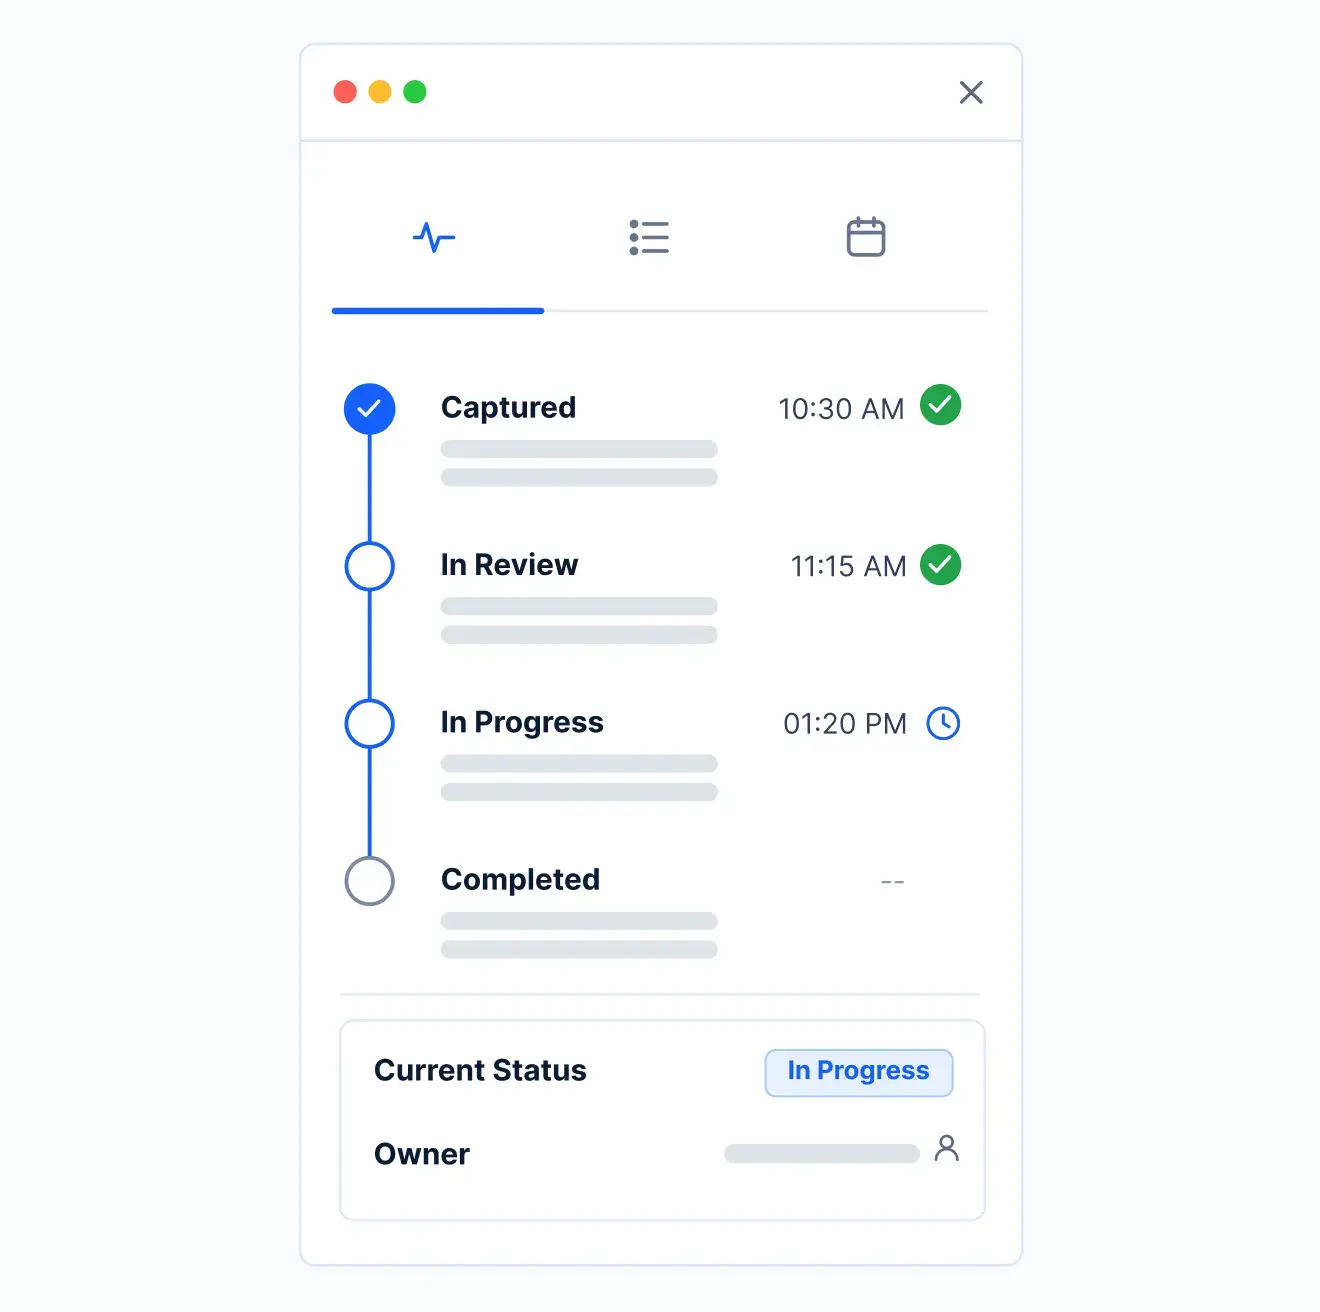
Once both approve, access is granted.
Record
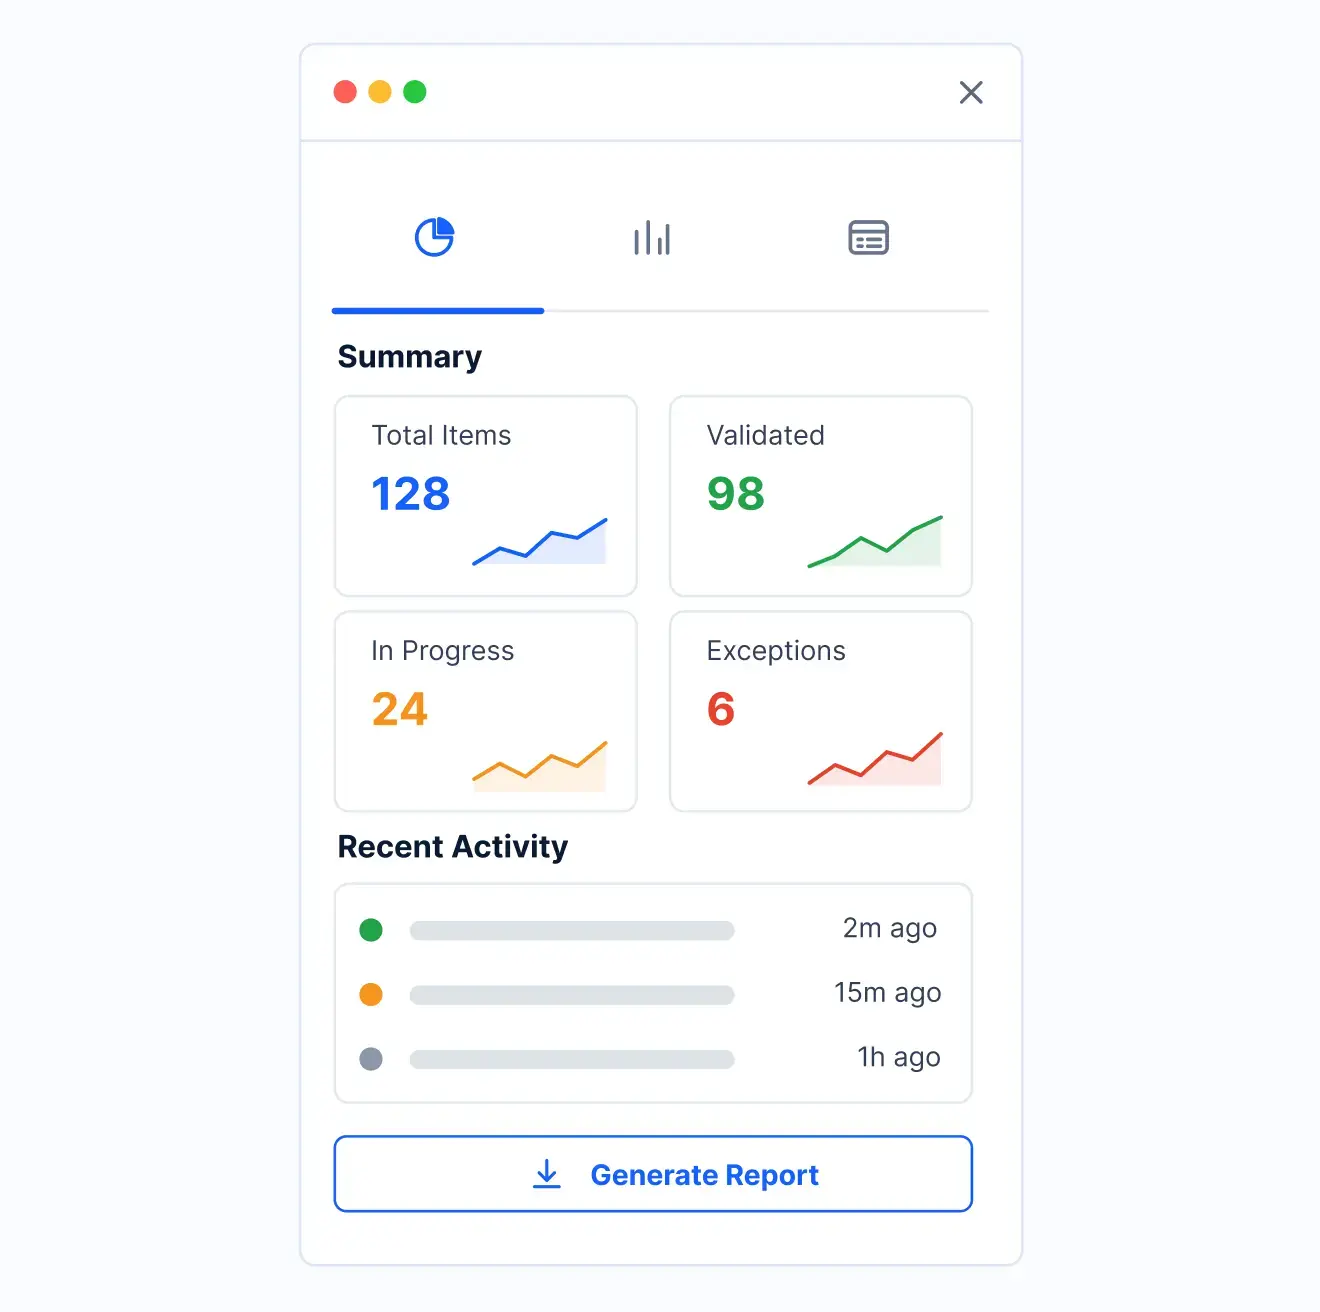
The entitlement register updates with who has access and why, access is recertified on a schedule, and a recorded role or employment change flags it for removal.
What changes when faculty entitlements run on Kissflow
| Process | Before Kissflow | On Kissflow |
|---|---|---|
| Access request | Requested informally by email, with inconsistent justification | Captured formally with a role or system-change trigger and justification |
| Approval routing | Approved by a manager alone, without the system owner's sign-off | Routed to both the manager and the owning system's administrator |
| Entitlement register | Scattered across individual system admin consoles | A single register of who has access to what and why |
| Periodic review | Reviewed only when an audit specifically asks | Recertified on a recurring schedule |
| Deprovisioning | Depends on someone remembering during offboarding | Flagged automatically when a role or employment change is recorded |
| SoD reporting | Conflicts discovered during an external audit | Surfaced on a dashboard before the audit asks |
Connects to your IAM platform, Banner, Workday, and Canvas
Kissflow does not replace your IAM platform, Banner, or Workday as the systems that hold the access itself. It is the governed request, approval, and review layer that decides what gets granted and when it gets revoked.




Built for how faculty access actually drifts over time
Access reviewed on a schedule, not forgotten
Standing entitlements are recertified on a recurring cycle instead of sitting unreviewed after the initial grant.
Deprovisioning that doesn't depend on memory
A role change or separation automatically flags the access that should follow it for removal.
Segregation-of-duties checked, not assumed
Conflicting entitlements, like the ability to both submit and approve the same transaction, surface before an audit finds them.
An ERP and IAM-adjacent governance layer
Your IAM platform, Banner, and Workday remain the systems holding the actual access. Kissflow governs the request, approval, and review around it.
Live before your next audit cycle
IT and security staff configure entitlement types, approval routing, and review schedules in the visual builder.
An access report ready before it's requested
Entitlement and SoD reporting is available on demand, not assembled from scratch when an auditor asks.
Related apps
Create and Update Banner Access Management System
Module-level Banner access requests with SoD checks, approval, and recertification.
Create and Update Canvas Access Management System
Term-scheduled Canvas access with approval routing and automatic deactivation.
Apply Remove Access Hold Management System
Approval-routed holds and releases with a full register and student-facing status.
We help higher education IT and security teams answer who has access to what, on demand
“If a company cannot enable everybody to use AI, they will never get the true benefit of AI. Platforms like Kissflow allow us to put that capability in the hands of our users in a safe way.”
Vagesh Dave
GVP & CIO at McDermott International, Ltd
See The Full Story
“Advanced automation of all processes is easy to set up. I cannot imagine how to manage workflows without this software.”
Tanay Tiwary
Global Head - Digitalization & Business Improvement
See the Full Story
“Kissflow supports rapid application development by building a working application prototype in the shortest amount of time.”
Maria Theresa Cabigon
CIO, SN Aboitiz Power Group
See The Full Story
See what Kissflow can do for you
Talk to usGot questions? We're here to help.
Get SupportThis governs employee-side system access, LMS, ERP modules, research systems, granted to faculty. The Apply Remove Access Hold Management System governs holds on student accounts that block registration or transcript release. Different population, different systems.
This is the umbrella governance layer covering the full range of systems a faculty member might need access to. The Canvas and Banner access apps are the system-specific implementations most institutions ask for by name, built on the same request-approve-review pattern.
A scheduled recertification cycle, plus an immediate flag whenever a role change, contract end, or separation is recorded.
No. Your IAM platform remains the system that actually holds and enforces the access. Kissflow governs the request, approval, and periodic review that decide what gets granted there.
Yes. Entitlement types, approval routing, and review schedules are configured in the visual builder, and the AI Builder can generate a starting workflow from a plain-language description of your access policy.
Through APIs and integration connectors, under single sign-on and role-based access, with every request, approval, and review written to an audit log.
Configuration and AI-assisted setup move rollout to weeks, without an IAM platform implementation project.
Kissflow is certified to SOC 1, SOC 2, SOC 3, and ISO/IEC 27001, supports HECVAT review for procurement, and is built to support FERPA and GLBA Safeguards obligations, with data residency options in the US, EU, APAC, and Oceania.